How Gloucestershire Businesses Can Build Layered Cybersecurity Defences: Lessons from Recent UK Cyber Incidents
26 September 2025
- Business IT Security
- Small Business IT
Introduction
This guide breaks down recent high-profile cyber incidents and translates them into practical, layered steps Gloucestershire businesses can take right now. If you run a local shop, professional services firm, or growing team anywhere in Gloucestershire, these lessons are for you.
Why this matters for Gloucestershire
Gloucestershire businesses – from independent retailers on the High Street to growing professional services firms on local business parks – face the same tactics used against big brands, just with tighter budgets and smaller teams. Attackers know this and often target small businesses expecting lighter defences. The good news: right-sized, layered controls dramatically reduce risk without breaking the bank.
What actually happened: confirmed attack vectors in recent incidents
- Jaguar Land Rover (JLR): Attackers exploited compromised credentials (potentially via infostealer malware or phishing) and/or vulnerable legacy systems, leading to major disruption and data exfiltration. [Industrial Cyber] [SecurityWeek] [The Guardian]
- Co-op: Ransomware attack attributed to the DragonForce group, targeting IT networks and disrupting payments and supply chain. [BBC] [TechInformed]
- Marks & Spencer (M&S): Ransomware attack attributed to the Scattered Spider group, disrupting online and in-store operations. [Beyond Identity] [The Hacker News]
- KNP (Northamptonshire transport company): Attackers gained access using a single weak password, allowing the Akira ransomware group to deploy ransomware, resulting in business collapse. [BBC] [Breached.Company]
- Oxford City Council: Unauthorised network access targeting legacy IT systems, exposing historic staff and election worker data. No ransomware reported. [Oxford City Council] [The Register]
What Gloucestershire businesses can learn from these incidents
Each of these breaches offers a lesson for local businesses:
- Jaguar Land Rover: Even global brands fall to credential theft and legacy vulnerabilities. For Gloucestershire small and medium businesses, this means strong password management, MFA everywhere, and regular updates are non-negotiable.
- Co-op: Ransomware can halt critical operations. Local businesses should prioritise robust backups, endpoint protection, and tested incident response plans.
- M&S: No business is too large or too small for ransomware. Training staff to spot phishing and locking down remote access are essential.
- KNP: One weak password can end a business. Use password managers, enforce complexity, and audit accounts regularly.
- Oxford City Council: Legacy systems are a prime target. Map your IT estate and prioritise upgrades or segmentation for anything old or unsupported.
The onion model: why layered security works
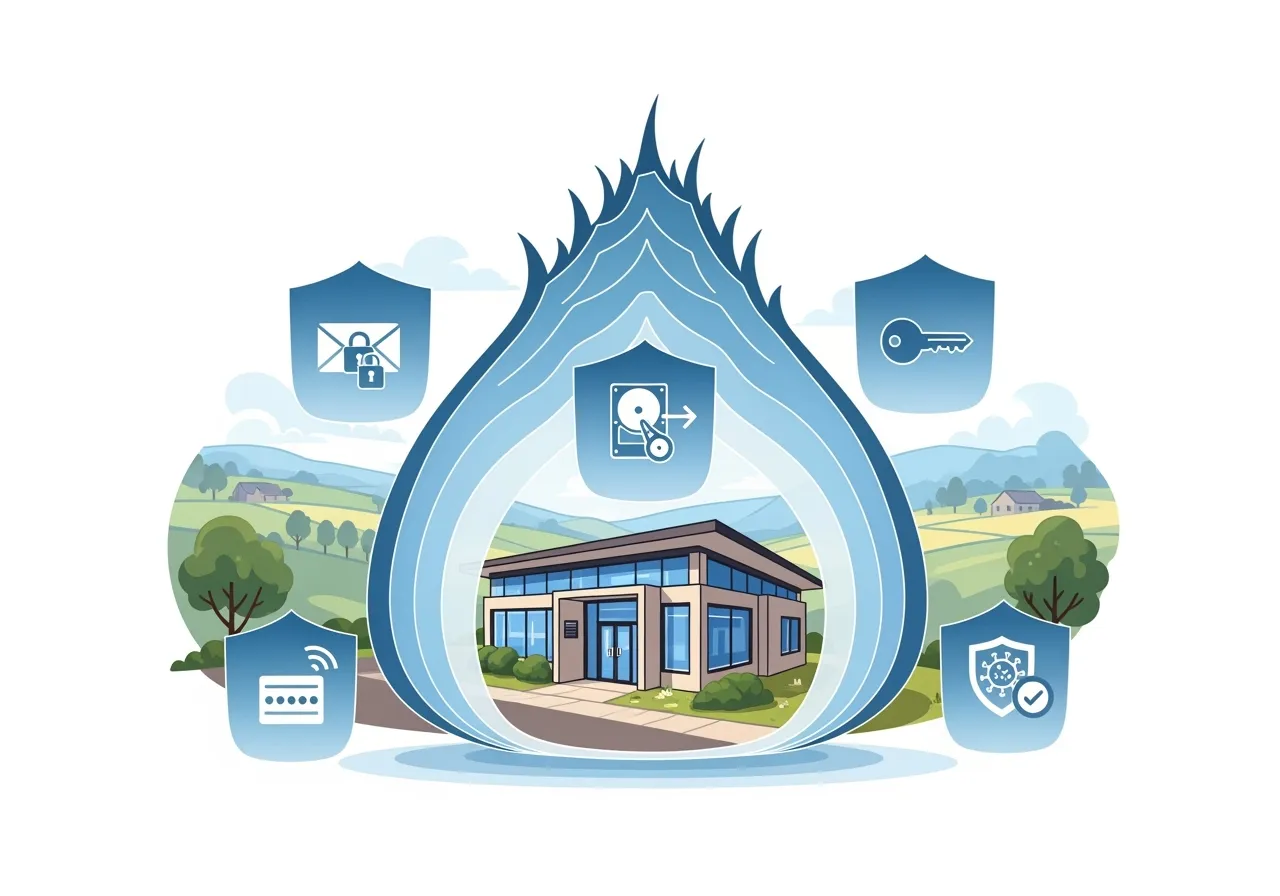
Think of your business like an onion. One thin outer layer will not stop a determined attacker – but multiple layers make progress slow, noisy, and easier to detect and contain:
- Outer layer – Human firewall: Ongoing awareness training, phishing simulations, and simple playbooks for staff. Teach stop, check, report.
- Email and web filtering: Advanced email security that uses AI or heuristics to detect malicious links or attachments and a safe browsing filter to block known-bad sites.
- Identity and access: MFA on all user or admin accounts; conditional access to restrict risky logins; disable legacy authentication; least privilege by default.
- Endpoint protection: Next-gen endpoint security (EDR) to detect suspicious behaviour, isolate infected devices, and roll back ransomware activity.
- Patch and vulnerability management: Keep operating systems, firmware, and apps up to date; scan for vulnerabilities and remediate by risk.
- Network segmentation: Separate guest and staff WiFi; isolate servers and backups; restrict east-west traffic so a breach does not spread.
- Data protection and backup: Encrypt data at rest and in transit; maintain immutable, offsite backups with tested restores; apply access controls and file-sharing restrictions.
- Monitoring and response: Centralised logging, alerting on suspicious sign-ins or privilege changes, and a simple incident response plan with clear roles and contacts.
Practical, right-sized protections for Gloucestershire businesses
Here is a concrete, affordable roadmap tailored to small and medium businesses in Gloucestershire (1 to 10 users), aligned with what we implement for clients:
- Microsoft 365 hardening: Enforce MFA for all users; disable IMAP or POP; set conditional access (block risky countries, require compliant devices); enable audit logging. Learn more: Microsoft 365 services
- Email security: Deploy enterprise-grade filtering for malware, phishing, and spoofing; implement SPF, DKIM, and DMARC with reject or quarantine policies. See our approach: Email security
- Endpoint security: Use a top-performing EDR or AV on all laptops or desktops; enable device encryption (BitLocker) and automatic updates. Protect endpoints: Endpoint protection
- Patch management: Apply OS or app updates weekly; prioritise zero-day fixes; track firmware updates on routers or firewalls. Manage updates: Management and monitoring
- Remote access hygiene: Prohibit direct RDP exposure; use a modern VPN with MFA; review firewall rules quarterly. Secure remote access: Network security
- Network basics: Segregate guest or staff WiFi; change default router passwords; disable unused ports or services; document the network. Get help: Networking
- Least privilege: Separate admin accounts; remove shared passwords; review access quarterly; adopt password managers. Start here: Cybersecurity
- Supplier access: Provide vendors with named accounts, MFA, and time-limited access; log their activity. Vendor security: Cybersecurity
- Security awareness: Quarterly bite-size training and phishing drills; publish a simple internal report suspicious email guide. User training: Cybersecurity
Backups that actually save the day
Backups are your last, vital onion layers – designed to survive when everything else fails:
- Immutable cloud backups: Back up Microsoft 365 (mail, OneDrive, SharePoint) to immutable, encrypted storage. Set retention to meet your needs (30 days minimum; longer for compliance). See options: Cloud backup
- 3-2-1 rule: Keep 3 copies of data, on 2 different media, with 1 copy offsite or immutable. Test restores monthly. Backup help: Backup services
- Scope clearly: Include cloud apps, on-prem servers or NAS, and critical endpoints. Document RPO or RTO (how much data you can lose, how fast you must recover).
- Recovery practice: Run tabletop exercises and random file restorations so you are confident under pressure.
Incident response: what to do when something feels wrong
- Isolate: If a device looks compromised, disconnect it from the network immediately.
- Reset and review: Force password resets; revoke tokens or sessions; check audit logs and admin changes.
- Restore carefully: Verify clean backups; rebuild infected machines; monitor closely after recovery.
- Report appropriately: Consider legal, regulatory, and client notifications (for example, ICO for personal data incidents). Get guidance: Cybersecurity
Quick self-check for Gloucestershire businesses
- Do all users and admins have MFA enabled everywhere?
- Is IMAP or POP disabled and are conditional access policies in place?
- Are guest and staff WiFi separated?
- Do you have immutable backups of Microsoft 365 and key systems, tested monthly?
- Is RDP closed to the internet and VPN protected by MFA?
- Are updates applied within days, not months?
Bringing it back to your Gloucestershire business
High-profile incidents at JLR, Co-op, M&S, KNP, and Oxford City Council are not outliers – they are signals. The same tactics used against big names are routinely aimed at smaller organisations in Gloucestershire because attackers expect lighter defences. The onion model works: stack multiple, sensible layers and you will frustrate intruders, spot problems faster, and recover cleanly.
About IT Consultancy, Services & Solutions Ltd
Based in Gloucestershire, we help small and medium-sized organisations put practical, affordable protections in place – because all businesses deserve great IT. Our philosophy is simple: let the techies manage the technology while you focus on your day-to-day business. With sensible layers and solid backups, you can reduce risk, spot problems faster, and recover cleanly.
Next steps – because all businesses deserve great IT
If you are in Gloucestershire or nearby and want practical help implementing these layers, we can harden Microsoft 365, secure endpoints and networks, and set up immutable backups that we test regularly – so you can operate with confidence.
Start with a quick chat and a plain-English action plan: Get in touch. Because all businesses deserve great IT.